Published 22 November 2026
To check whether a DNS change has reached your website, query the domain’s authoritative name servers and compare their answers with a few public DNS resolvers. Then test the website and email separately. A changed value in a DNS dashboard confirms only that the edit was saved there; it does not prove that every resolver has the new answer or that the destination service is configured correctly.
This distinction is useful during a hosting move, when updating an A or AAAA record, or when changing a mail-related record. It helps website owners avoid repeatedly editing records when the real problem is a wrong value, an unexpected DNS provider or an unconfigured destination.
What “DNS propagation” means in practice
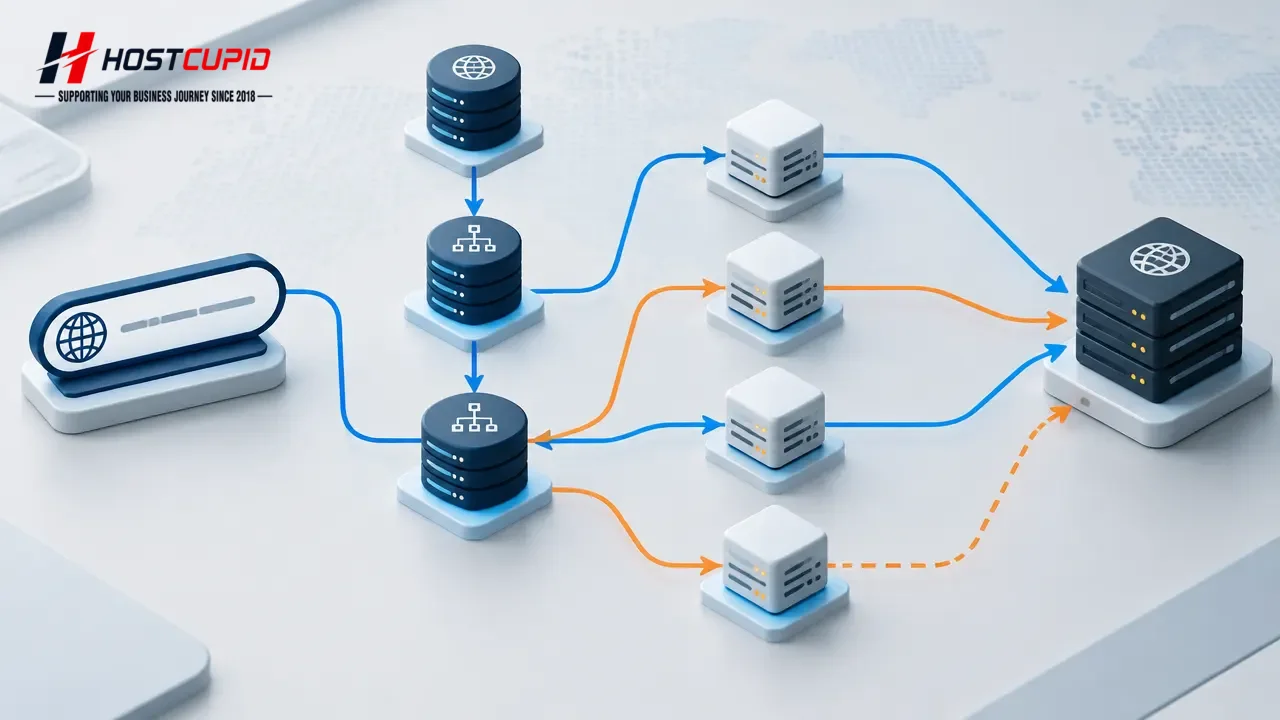
DNS resolvers look up records such as A, AAAA, CNAME and MX on behalf of users. A resolver may keep a previous answer in its cache until that answer’s time to live, or TTL, expires. As a result, two resolvers can temporarily return different answers for the same name.
DNS is delegated through a hierarchy. The registrar identifies the domain’s name servers; those authoritative name servers publish the zone records. If the domain uses a third-party DNS provider, changing a record at the hosting account may have no effect unless those name servers actually serve that zone. First identify which name servers are authoritative for the domain.
Important: Different lookup results do not automatically mean that DNS is broken. Check which server was queried, which record type was requested and whether the differing answer could still be cached.
Before testing: record the intended change
Write down the hostname, record type, intended value and TTL before troubleshooting. For a web move, confirm the destination IP address with the new hosting provider. For mail, note the required MX destination and any TXT records the mail service asks you to publish. Do not guess values or copy records from an unrelated domain.
- Check the DNS provider: Find the name servers currently delegated for the domain, then edit the zone at the provider that operates them.
- Check the exact name: The root domain, such as example.in, is not the same hostname as www.example.in or mail.example.in.
- Check the record type and value: A records point to IPv4 addresses; AAAA records point to IPv6 addresses; CNAME records point to another hostname. MX records direct mail.
- Save the old values: Keep a record of the previous settings so you can identify the change or restore the earlier configuration if needed.
How to check DNS answers step by step
- Look up the authoritative name servers. Use a DNS lookup tool or command-line utility to find the domain’s NS records. Confirm that they match the DNS provider where you made the edit. If they do not, the edit was probably made in a zone that is not currently authoritative.
- Query an authoritative server directly. Use a DNS utility such as
digto request the relevant record from one of the listed name servers. For example,dig @ns1.example-dns.com example.in Arequests the root domain’s A record from that server. Replace the example name server and domain with the real values. On systems withoutdig, use an equivalent DNS lookup tool. - Compare other resolvers. Check the same hostname and record type through more than one public recursive resolver. A recursive resolver may return a cached answer, while the authoritative query shows what the zone currently publishes. Record the answers and the TTLs shown by your tool.
- Repeat for relevant hostnames and types. Check both the root domain and www if both should work. If mail is affected, inspect MX records and the necessary mail-related TXT records separately; a successful website lookup does not confirm that email is configured properly.
- Test the service itself. Open the website over HTTPS and check that the intended site loads with a valid certificate. Send a test email to and from an address on the domain if mail settings changed. DNS can point to a destination even when the website, certificate or mail service is not ready.
Read the results before changing anything
| What you find | What it may mean | Next check |
|---|---|---|
| Authoritative answer has the old value | The edit may be in the wrong DNS zone, unsaved or incorrect. | Confirm delegation and inspect the record at the active DNS provider. |
| Authoritative answer is new; a resolver is old | The resolver may have a cached answer. | Compare TTLs and check again later rather than repeatedly editing the record. |
| Resolvers agree, but the site fails | The destination service, web-server configuration, firewall or TLS certificate may need attention. | Test the destination directly and review its hosting configuration. |
| Website works, but email fails | Mail routing or mail authentication may be wrong or incomplete. | Check MX and required TXT records against the mail provider’s instructions. |
Common mistakes and safe follow-up
Repeatedly changing an address while cached answers remain can make troubleshooting harder. A low TTL set shortly before a planned move may reduce how long some cached answers persist, but it cannot force every resolver to refresh immediately. Plan changes ahead, verify the destination before switching records, and allow time for caches to expire.
Also avoid assuming that a DNS lookup proves the website is ready. The new host must have the site files, database, domain configuration and HTTPS setup it needs. During a migration, testing the destination before changing public DNS can catch service problems without involving visitors.
For a domain hosted through HostCupid, this check is relevant when coordinating a website migration or reviewing a DNS change: identify the active DNS provider, compare the published records with the intended destination, and test the website and email as separate services. HostCupid is a Chennai-based provider of shared, WordPress and reseller hosting, website development and migration assistance; the DNS lookup itself remains useful regardless of which provider operates the domain.
For command behaviour and DNS concepts, consult the Google Public DNS usage documentation and Google’s DNS-over-HTTPS documentation. If results disagree, keep a short record of the time, resolver, queried name and returned value. That evidence helps distinguish a cached answer from a zone or destination configuration problem.
Sources